
Supervisory evidence
Inspections ask for proof that controls operate, not only that policies exist.
No suggestions match. Press Enter to search the whole site.
Banks, NBFCs, insurers, capital market intermediaries and fintechs operate under close regulatory scrutiny. We help them engineer controls that satisfy supervisors and hold up in production.
The obligations are well known. The difficulty is proving, continuously, that controls operate as described.
Inspections ask for proof that controls operate, not only that policies exist.
Outsourced services and cloud platforms extend the perimeter the regulator holds you accountable for.
Staff and developers are already using AI with customer and financial data.
Incidents must be detected, contained and reported within tight timelines.
Select any capability to see the offerings.
Rhinexa Niyantran detects Indian identifiers such as Aadhaar, PAN, UPI and IFSC in AI prompts and responses, applies identity-based policy, and records signed evidence of each decision.
Explore Rhinexa Niyantran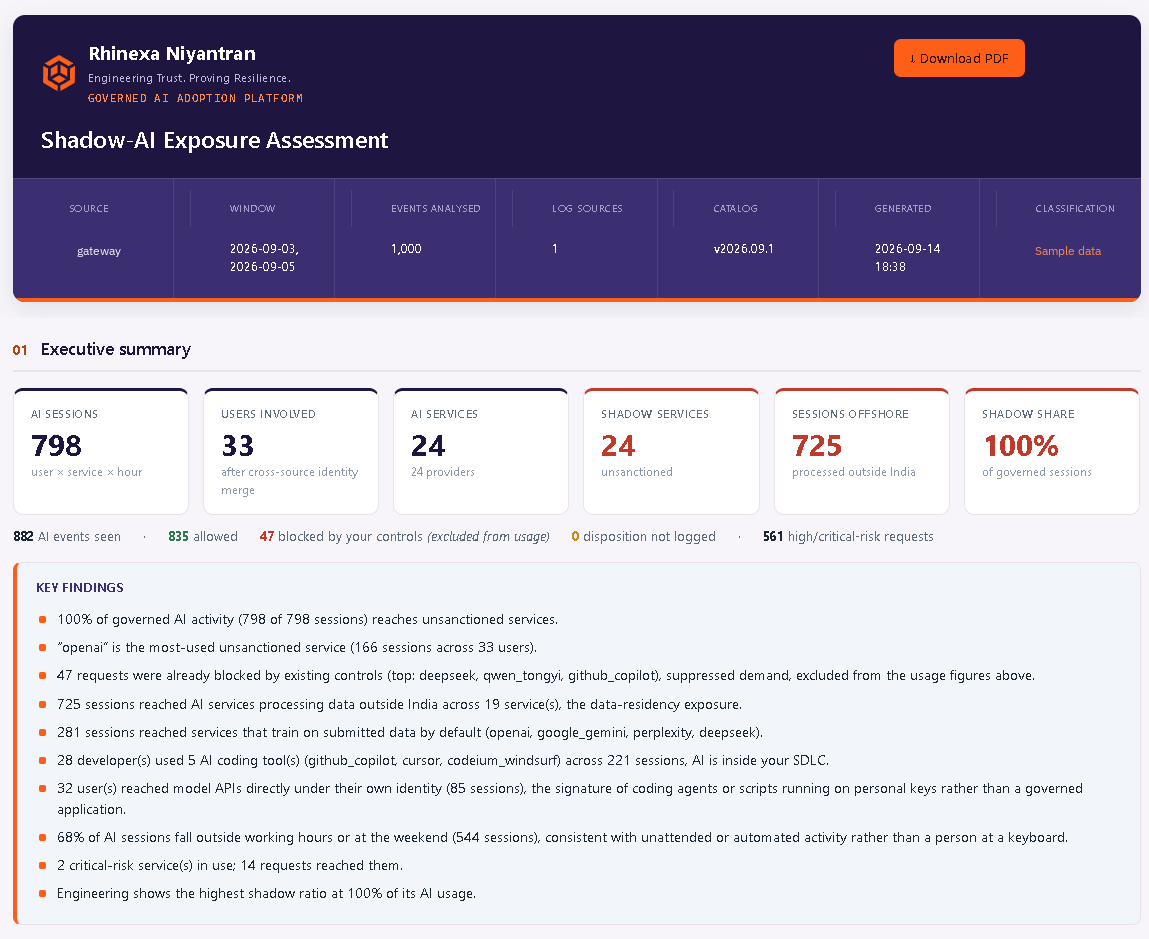 Sample data
 AI Security
Enterprise AI is moving from answering questions to taking actions. The security model has to follow.
 Governance, Risk and Compliance
Why asset clarity is a board-level risk decision: visibility, ownership and accountability before tools.
 SIEM and SOC
Drowning in alerts is not a detection strategy: five deployment mistakes and what SIEM plus SOAR changes.
A guided demo, then a pilot with acceptance criteria agreed up front.
Request a demoTell us what you are working on and we will put you in touch with the right practice.
Contact us