
SIEM strategy and use cases
What the platform must detect for your business, the log sources that reveal it, and the response each detection triggers.
No suggestions match. Press Enter to search the whole site.
Modernise detection, response and security operations. We design and build the SIEM, engineer the detections, automate the response and enable your team to run it. We do not operate a monitoring service, and we say so.
Most estates have a SIEM. Few get decisions out of it: thousands of daily alerts, logs in silos, events without context and analysts sifting by hand while the clock runs. The platform was deployed with default rules for a non-default estate, and nobody defined what it must detect.
A SIEM earns its keep by deciding: which event matters, how much, and what happens next. Making it decide is engineering work, and it is the work we do.
Take one offering on its own, or combine them into a programme with a named lead and agreed exit criteria.
What the platform must detect for your business, the log sources that reveal it, and the response each detection triggers.
Platform selection where needed, log source onboarding, normalisation, retention and cost control on the platform you own.
Correlation rules, behavioural baselines and tuning until alerts are believable, with coverage mapped to attacker techniques.
Containment, suspicious-login investigation, phishing response and enrichment automated, so analysts spend their time on judgement.
Roles, runbooks, drills and metrics for your own team, whether in-house or with a provider you choose.
The technique is run, the SIEM is checked, the gap is closed: purple teaming as a routine, not an event.
A named practice lead from scoping to close, with deliverables agreed before work starts.
Objectives, use cases and the sources that serve them.
Log sources onboarded, rules customised, thresholds refined.
Playbooks for the repetitive; integration across endpoint, cloud and network tools.
Drills, threat intelligence refreshed, rules tuned from real incidents.
Measured outcomes from real engagements will be published here once clients consent.
Noise measured and cut, so the alerts that fire are the ones that matter.
Detection to containment shortened by automation your analysts trust.
Detections mapped to techniques and validated, with the gaps on a plan.
Passive network detection and correlation, with a tamper-evident record of what happened, forwarded to your SIEM.
Explore Rhinexa Sentinel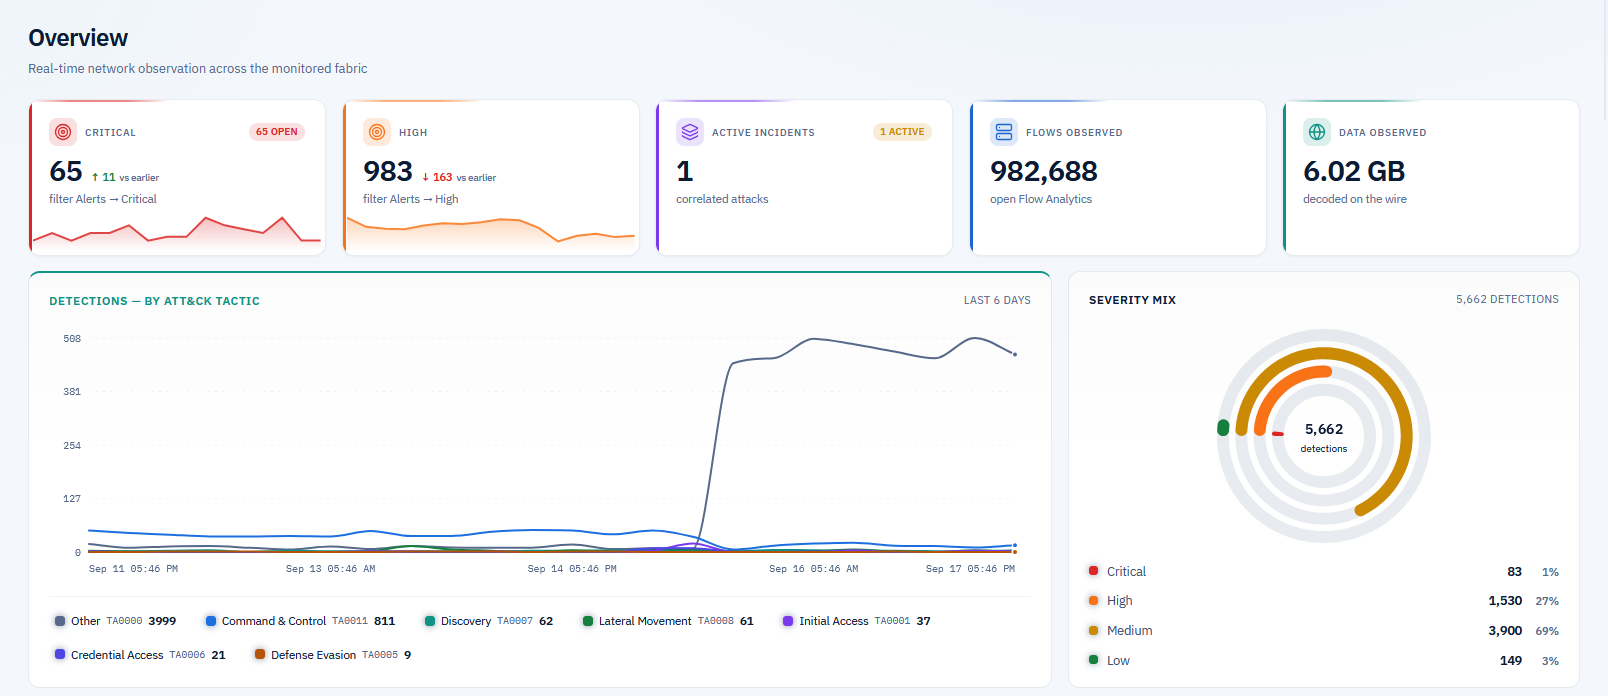 Sample data
Drowning in alerts is not a detection strategy: five deployment mistakes and what SIEM plus SOAR changes.
Read the perspectiveTell us what you are working on and a practice lead will respond.
Contact the practice