
Cloud security architecture
Landing zones, guardrails and identity boundaries for public and private cloud, designed before the workloads arrive.
No suggestions match. Press Enter to search the whole site.
Harden cloud, data centre and hybrid estates, and keep them hard. We baseline, engineer and assure the controls your platforms depend on, with the evidence to show they still operate.
A hardened baseline is a starting point. Cloud accounts multiply, containers ship daily, on-premises systems outlive their owners, and the configuration that passed the last audit is not the configuration running today. Most incidents in the estate are not exotic; they are a control that was installed once and never run.
Infrastructure security is a lifecycle: observe, tune, enforce, review. The work is making that lifecycle routine, across every platform you own, with evidence that does not depend on someone remembering to check.
Take one offering on its own, or combine them into a programme with a named lead and agreed exit criteria.
Landing zones, guardrails and identity boundaries for public and private cloud, designed before the workloads arrive.
Baselines against CIS Benchmarks, expressed as policy code, with drift detected and reported rather than discovered in an audit.
Prioritised by exposure and business criticality, with fix times measured and reported.
Least privilege, MFA and privileged access management for the infrastructure itself, not only for the applications on it.
Web application firewalls, load-balancer and DDoS controls selected, tuned and run to a baseline, as in our own estate.
Backup, recovery and disaster recovery tested against agreed objectives, so recovery is proven rather than assumed.
A named practice lead from scoping to close, with deliverables agreed before work starts.
Inventory the estate, measure it against benchmarks and map exposure to the services it supports.
Order the work by business criticality and exposure, not by tool category.
Engineer the controls with your platform teams and automate what can be automated.
Continuous configuration assurance, with evidence that controls still operate.
Measured outcomes from real engagements will be published here once clients consent.
Baselines enforced as code, drift caught between audits rather than by them.
Objectives tested, not stated in a policy.
Inventory, health and exposure connected to the business services that depend on them.
Discovery, health, topology, traffic and alerts for the whole estate, self-hosted, with no agents on devices.
Explore Rhinexa NMS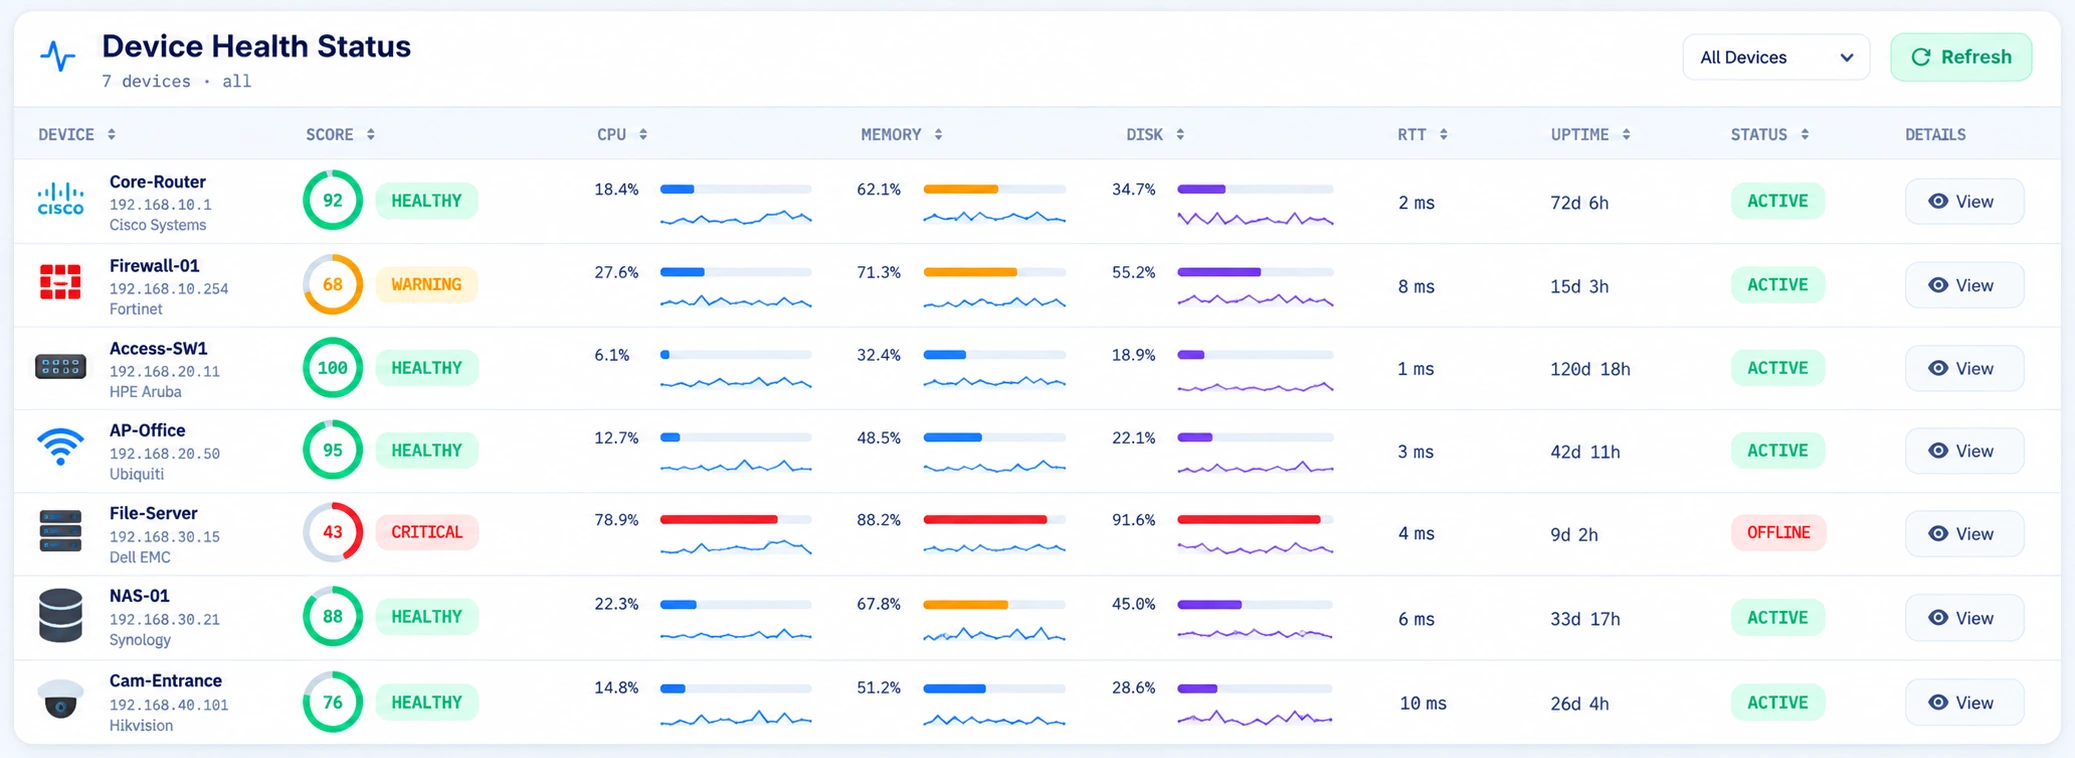 Sample data
What a year of running a machine-learning WAF at the load-balancer layer taught us about hardening as a lifecycle.
Read the perspectiveTell us what you are working on and a practice lead will respond.
Contact the practice