
Flowed-down obligations
Client contracts carry security schedules that must be evidenced, often across several frameworks at once.
No suggestions match. Press Enter to search the whole site.
Product companies and global capability centres inherit their clients' security obligations, ship software daily and were the first to put AI in the hands of every developer. We help them prove control at the speed they deliver.
Every client audit asks the same questions. The answer has to come from the pipeline, not from a spreadsheet.
Client contracts carry security schedules that must be evidenced, often across several frameworks at once.
Developers use AI with source code every day; the question is whether policy and evidence follow.
Offshore delivery models need access tied to identity and purpose, with an audit trail clients can inspect.
Security has to run inside the delivery pipeline or it becomes the queue at the end.
Select any capability to see the offerings.
Rhinexa Niyantran applies per-action policy to what a managed coding agent may run, read, write or call, live today for Claude Code and Codex, and records every decision as signed evidence.
Explore Rhinexa Niyantran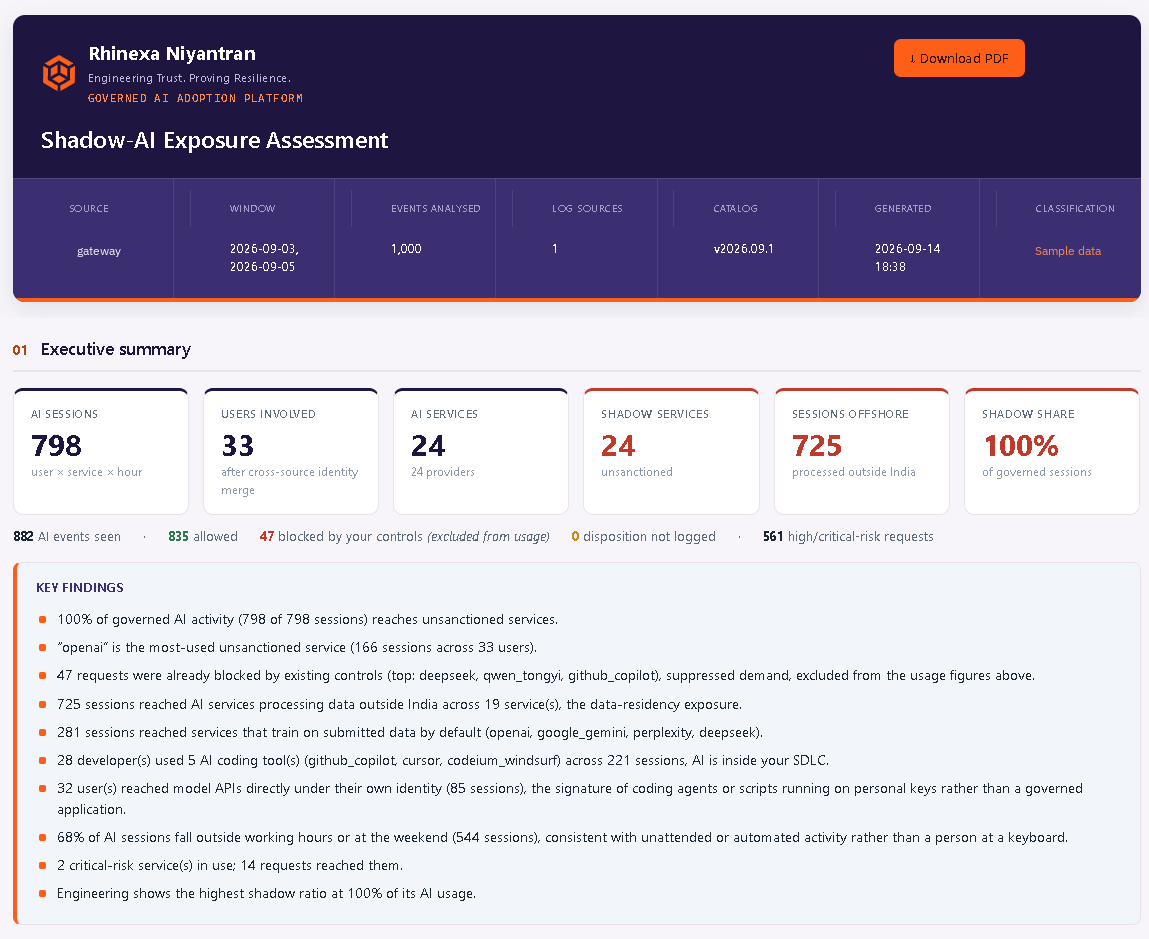 Sample data
 AI Security
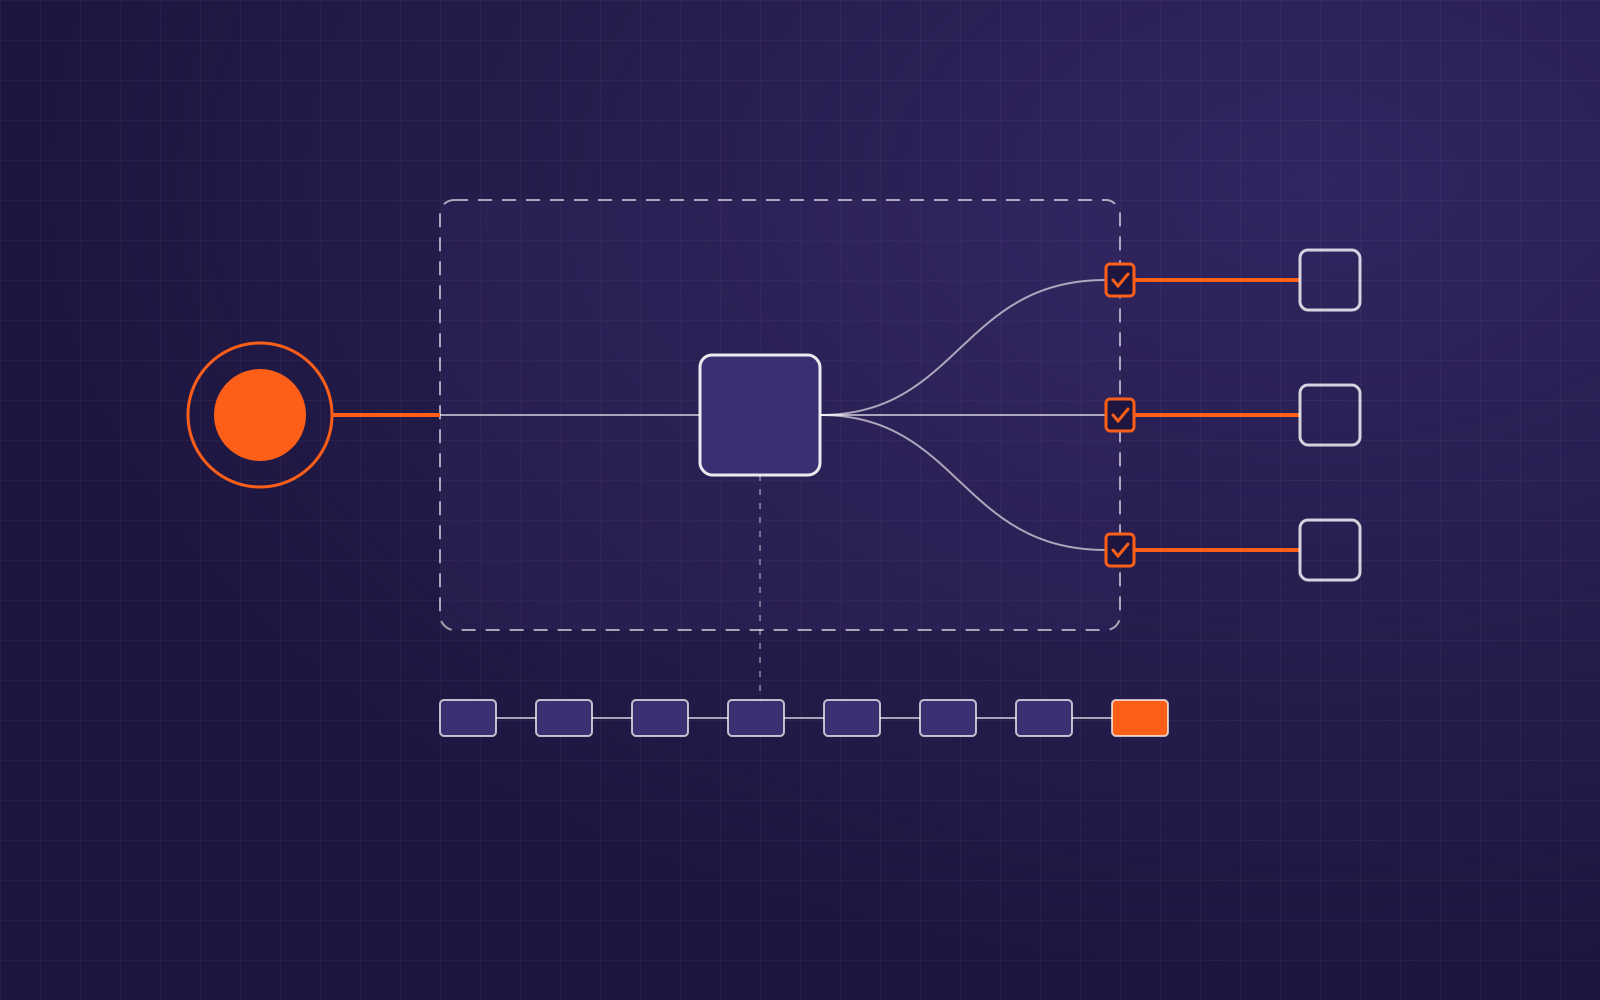
Enterprise AI is moving from answering questions to taking actions. The security model has to follow.
 Application Security
Security that begins in the planning room costs a fraction of security that begins in the incident room.
 Purple and Red Teaming
Functional testing proves the application works. Security testing proves it survives.
A guided demo, then a pilot with acceptance criteria agreed up front.
Request a demoTell us what you are working on and we will put you in touch with the right practice.
Contact us