
Architecture and segmentation
Zero-trust network design, segmentation and micro-segmentation planned around business services and their trust boundaries.
No suggestions match. Press Enter to search the whole site.
Protect connectivity across every trust boundary. Segmentation, transport controls and passive detection, designed layer by layer and tested end to end, including the industrial networks most tools cannot touch.
Most estates have firewalls, TLS and MFA. Fewer can say who owns the controls at each layer of the network, when they were last tested end to end, and which business process stops if a layer fails. Attackers do not need a layer with no control; they need one with no clarity.
Network security is seven stacked decisions, from physical access to application traffic, and increasingly it has to include the east-west traffic between your own systems and the industrial or clinical networks where nothing can be probed.
Take one offering on its own, or combine them into a programme with a named lead and agreed exit criteria.
Zero-trust network design, segmentation and micro-segmentation planned around business services and their trust boundaries.
Rule review, cleanup and change control across every vendor you run, so the rule base is one you can defend.
Access to the estate tied to identity and device posture rather than to the network a user happens to be on.
Rhinexa Sentinel deployed from a mirror port, tuned to your estate, and forwarded into the SIEM and workflows you already run.
Zones and conduits in the IEC 62443 model, mirror-only visibility, and controls that cannot become a risk to the line.
Segmentation, transport, session and wireless controls tested as an attacker would test them, with the findings mapped to owners.
A named practice lead from scoping to close, with deliverables agreed before work starts.
Layers, flows, owners and the business processes behind them, in one view.
Target segmentation and control set per layer, with the evidence each must produce.
Engineer the controls under your change process, vendor by vendor.
Test end to end, then repeat as the estate changes.
Measured outcomes from real engagements will be published here once clients consent.
Boundaries designed around business services and tested, not drawn once.
Every rule with an owner and a reason, reviewed on a cycle.
Independent network records that survive when host logs do not.
Passive detection and correlation from a copy of your traffic, with a tamper-evident record. Never in the path.
Explore Rhinexa Sentinel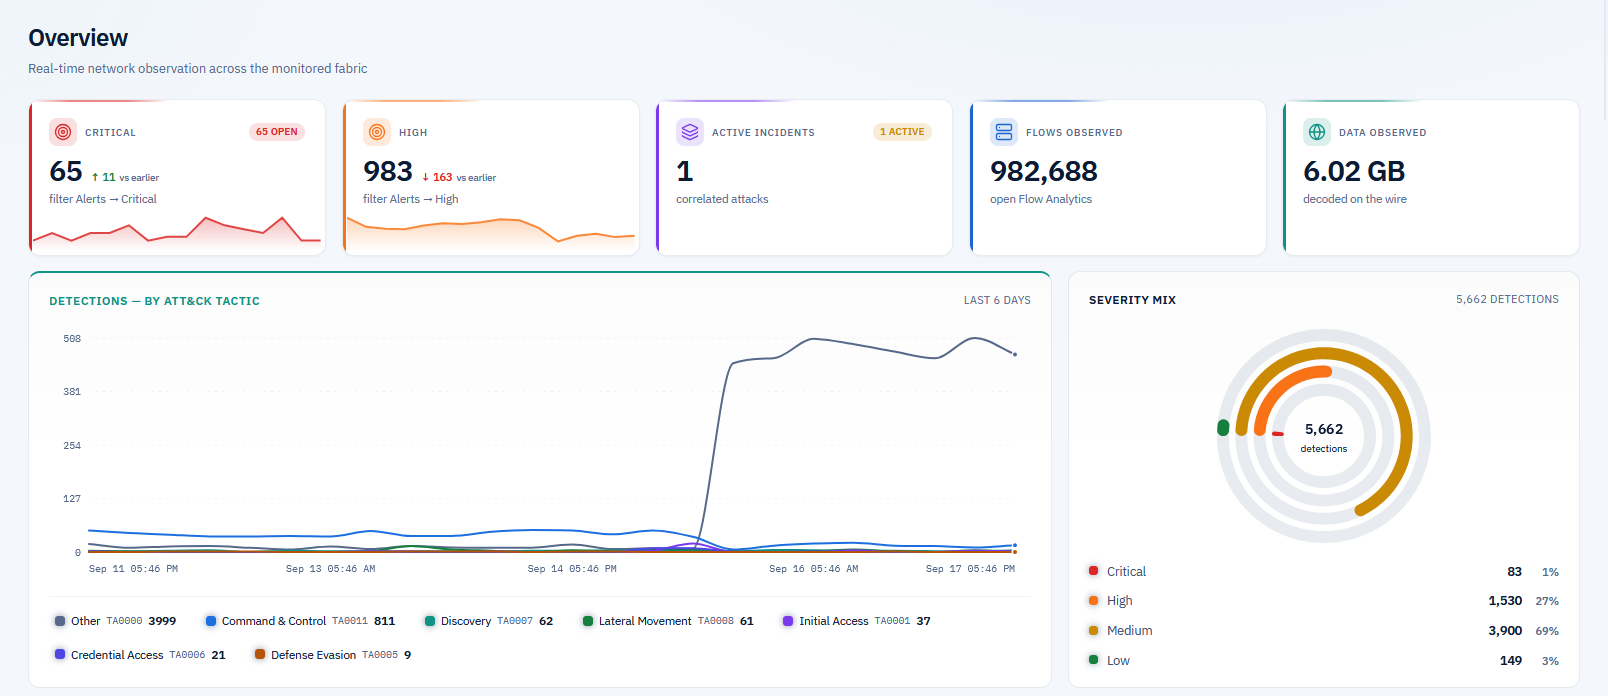 Sample data
The control existed, just not at the layer that got hit. Defence in depth is seven audits.
Read the perspectiveTell us what you are working on and a practice lead will respond.
Contact the practice