
Cyber asset governance
Identify, classify and prioritise the estate, with named business, technical, data, control and risk owners for what matters.
No suggestions match. Press Enter to search the whole site.
Turn obligations into continuous control assurance. We connect assets to owners, owners to controls and controls to evidence, so compliance is a state you are in rather than a season you prepare for.
The quarter ends, the audit approaches, and teams scramble to collect evidence that should have existed all along. The risk register lists incidents, not assets. Controls exist on paper; whether they operate today is anyone's guess.
Governance that works starts with a list: what exists, what matters, who owns it, and what happens when it fails. From there, obligations map to controls, controls produce evidence, and the audit becomes a report rather than an event.
Take one offering on its own, or combine them into a programme with a named lead and agreed exit criteria.
Identify, classify and prioritise the estate, with named business, technical, data, control and risk owners for what matters.
Scope, risk assessment, statement of applicability and control operation, ready for your certification body. We prepare; auditors certify.
DPDP Act, RBI, SEBI and IRDAI directions, CERT-In directions and sector rules mapped to the controls you run. Mapping supports assurance; it is not certification.
A register that ties to assets and business consequence, an agreed appetite, and reporting a board can act on.
Policy to control to operation to evidence, automated where the systems allow, so evidence accumulates instead of being assembled.
Suppliers assessed by the consequence of their failure, with obligations flowed down and evidence collected on a cycle.
A named practice lead from scoping to close, with deliverables agreed before work starts.
Scope, obligations, assets and owners agreed in writing.
Every obligation to a control, every control to an owner and a source of evidence.
Controls run on a cycle, with exceptions managed rather than hidden.
Continuous collection, so the next audit starts from a report.
Measured outcomes from real engagements will be published here once clients consent.
Risk reported against what fails and what it costs, not against incident counts.
Evidence collected as controls operate, not reconstructed under deadline.
Exposure, ownership and progress in one page.
Every policy decision on AI use recorded as signed, hash-linked, tamper-evident evidence you can verify offline.
Explore Rhinexa Niyantran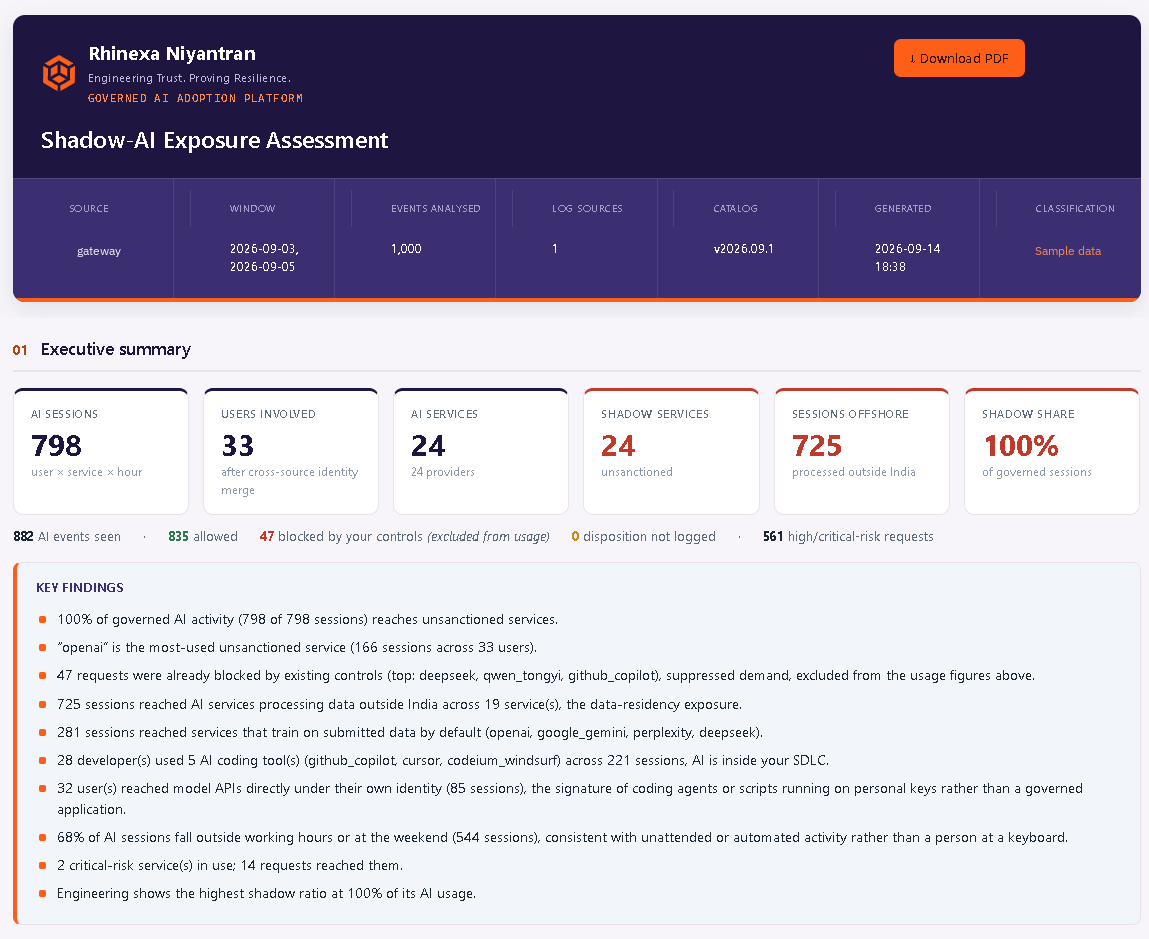 Sample data
Why asset clarity is a board-level risk decision: visibility, ownership and accountability before tools.
Read the perspectiveTell us what you are working on and a practice lead will respond.
Contact the practice